At present, there are many cases related to Zhangjiajie tourism in many places, and corresponding control requirements have been issued one after another.

CCTV News:At present, there are many cases related to Zhangjiajie tourism. According to the introduction of Sichuan Health and Wellness Commission, two of the three newly confirmed local cases in Sichuan have traveled to Zhangjiajie on the 28th.

In addition, last night (July 28), a press conference on epidemic prevention and control was held in Chengdu, Sichuan Province, and it was also reported that at 21: 00 on July 27 — At 18: 00 on July 28th, 5 newly reported local confirmed cases and 1 local asymptomatic infected person in Chengdu were all related to the living history in Zhangjiajie, Hunan.
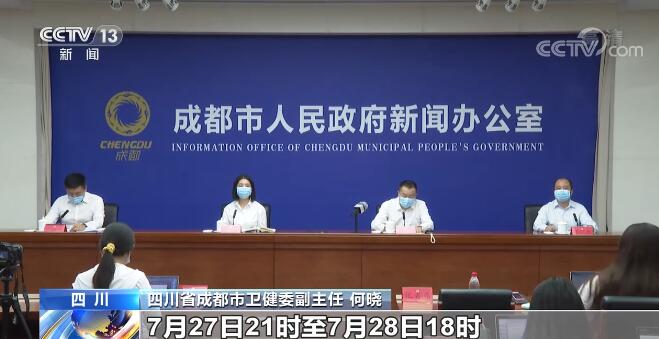
He Xiao, Deputy Director of Chengdu Health and Wellness Commission, Sichuan Province:21: 00 on July 27th — At 18: 00 on July 28th, Chengdu newly reported 5 local confirmed cases and 1 local asymptomatic infected person. Among them, 5 people came to (returned to) Rong in Zhangjiajie City, Hunan Province, and 1 person was an associated case.

After the outbreak, Chengdu immediately launched the emergency plan for epidemic prevention and control, and quickly carried out the flow tracing. As of 18: 00 on July 28, the city has tracked 203 close contacts of confirmed cases in Rong, of which 66 were negative for nucleic acid, and the rest of the results are pending; In addition, nucleic acid tests have been carried out on key personnel and the environment. Nucleic acid sampling and investigation were carried out in Qingyang District, High-tech Zone and Tianfu International Airport overnight.
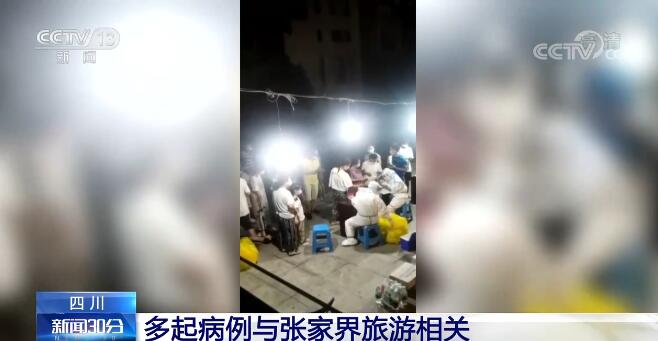
       He Xiao, Deputy Director of Chengdu Health and Wellness Commission, Sichuan Province:From 15: 00 on July 28, 2021, Xi ‘an Community, Youpin Road, Qingyang District, Chengdu, and Yasongju Community, the capital of High-tech Zone, were designated as medium-risk areas, and residents in the areas were required to strictly implement home isolation, stay indoors and close management. At the same time, the area adjacent to the medium-risk area shall be sealed and controlled, and personnel can only enter and leave, and gathering is strictly prohibited. People who have lived in Zhangjiajie since July 17th should take the initiative to report to their communities, units and hotels, and cooperate with the local authorities to implement various prevention and control measures such as nucleic acid detection, isolation control and health monitoring in Covid-19 as soon as possible.       

The Beijing Municipal Health and Wellness Commission reported today that a newly confirmed case on the 28th was also related to Zhangjiajie tourism. The case traveled to Zhangjiajie and other places in Hunan on July 20th, returned to Beijing on the 25th, and developed fever and other symptoms on the 26th. The result of nucleic acid test was positive on 28th, and the diagnosis was made on the same day.

The address of the case is the second district of Longyueyuan, Huilongguan, Changping District, Beijing. Beijing has carried out epidemiological investigation on the above-mentioned confirmed cases and implemented control measures as required.

The audience at the 18 o’clock performance of "Charming Xiangxi" in Zhangjiajie on July 22 is a high-risk group. Please report immediately.

In view of the fact that many cases are related to Zhangjiajie tourism, some cases have seen Zhangjiajie’s "Charming Xiangxi" performance, and the Zhangjiajie epidemic prevention and control headquarters released a message that the first performance of Zhangjiajie’s "Charming Xiangxi" on the evening of July 22, that is, all the audiences in the 6: 00 to 7: 00 show belong to high-risk groups.
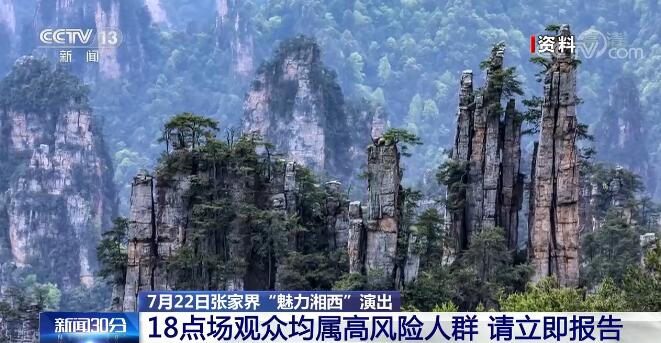
At present, according to this information, various localities have issued control requirements one after another. Recently, people who have lived in Zhangjiajie, especially those who have watched the performance in the "Charming Xiangxi" theater, should take the initiative to report to the local community or disease control institutions.
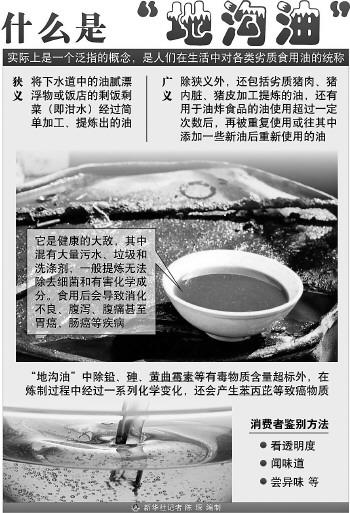
Identify gutter oil and try these tricks.

  Studies have shown that long-term intake of waste oil will cause obvious harm to human body, such as developmental disorders, enteritis, hepatomegaly, heart and kidney enlargement and fatty liver. Aflatoxin, one of the main hazards in gutter oil, is a strong carcinogen, and its toxicity is 100 times that of arsenic. Another question is ethical. Can you eat the oil that others have eaten, which goes bad in the sewer and is fished out again?
  So, is there a simple way to identify gutter oil? We might as well listen to what food science experts and insiders say.
one
There is no good way to scientifically identify waste oil at present.
  In an era of paying attention to food safety, the ideal state is that when you go to a restaurant, you take out a test paper and dip it in the dish. After a while, you take it out and compare it with the spectrum table, and then shout, "Boss, change the oil!"
  However, the reality is that up to now, scientists have not found an ideal means to detect and identify gutter oil.
  "Oil mixed with oil, fairy sorrow, fairy is difficult to separate it. Waste cooking oil has a history of more than 20 years. Even today, we can still see waste cooking oil in rural markets and urban-rural junction markets, and we also feel that it has entered the dining hall. If calculated by tonnage, there should be millions of tons of waste oil digested every year. I am very embarrassed. We can’t find a very effective technical means to identify it. This oil is gutter oil, and this oil is not gutter oil. " When attending a CCTV program, Hu Xiaosong, vice president of the College of Food Science and Nutritional Engineering of China Agricultural University, once said this.
  Hu Xiaosong pointed out that the current detection methods have not overcome this technology and cannot scientifically distinguish the quality of oil, but the Ministry of Science and Technology has set up a special project for this matter, and I believe that it will be possible to distinguish the quality of oil by scientific means in the near future.
2
Traditional detection methods have certain limitations.
  In the view of scientific researchers, the difficulty in treating gutter oil lies in that it is difficult to distinguish gutter oil from ordinary oil only from appearance and sense after refining processes such as washing, distillation, decoloration and deodorization. Illegal traders will also mix waste oil into edible oil, and if the content is small, it is even more difficult to detect.
  He Dongping, a professor at the School of Food Science and Engineering of Wuhan Institute of Technology, has been engaged in the research of gutter oil for many years. In He Dongping’s view, the traditional detection methods only grasp a certain characteristic of gutter oil, and no method can effectively detect gutter oil from different sources at the same time, which sometimes leads to a large detection error and more possibility of misjudgment.
  Wang Le, a graduate student of Wuhan Institute of Technology, once developed a blue test paper. With the increasing proportion of waste oil, the blue test paper will show yellow-green, light yellow and bright yellow. This is based on the "accumulation" of oil to detect the purity of oil, but this method is also limited by the proportion of waste oil added.
  On the Internet, you can find a company specializing in the production of "Quick Detection Kit for Waste Oil", but from the instructions provided by the company, "for some unpurified oils (such as sesame oil, pepper oil, etc.) and oils with other ingredients (such as Chili oil), this method is easy to produce false positives".
three
Identify the waste oil refrigerator?
  Senior chef Feng Peng, who once worked as a chef and executive in many big restaurants in Beijing, said that under normal circumstances, gutter oil and ordinary oil can’t be distinguished, and it is inevitable to be fooled when purchasing. He can only judge by practice: restaurants usually need to oil before cooking. In this "lubricating oil" process, good oil can be used seven or eight times repeatedly, while waste oil will become sticky and have a spicy taste after being used for up to three times.
  "In addition, when the outdoor temperature is low, waste oil will solidify like palm oil, so people often use waste oil to pretend to be palm oil." Feng Peng said that gutter oil can be identified in winter and can be tested in the refrigerator in summer. Some media think that gutter oil has a taste and can be smelled out. In addition, it contains a lot of water, and the pot will explode. Feng Peng thinks these are nonsense, because water can’t be mixed into oil at all, and gutter oil has no odor.

four
How should we identify waste oil?
  Take a look. Look at the transparency, pure vegetable oil is transparent, and the transparency will decrease due to the mixing of alkali grease, wax and impurities in the production process; Look at the color, pure oil is colorless, and the oil will be colored because the pigment in the oil is dissolved in the oil in the production process; Look at the sediment, its main component is impurities.
  Second smell. Each oil has its own unique smell. You can drop a drop or two of oil on your palm, rub your hands together, and smell it carefully when you are hot. Oil with odor indicates that there is a problem with the quality, and it is likely to be waste oil with odor; If there is a smell of mineral oil, you can’t buy it.
  Three tastes. Take a drop of oil with chopsticks and taste it carefully. The oil with sour taste is unqualified, the oil with bitter taste has been rancid, and the oil with peculiar smell may be waste oil.
  Listen. Take one or two drops of oil from the bottom of the oil layer, coat it on flammable paper, light it and listen to its sound. The products with normal combustion and no noise are qualified products; If the combustion is abnormal and makes a "squeaky" sound, the water content exceeds the standard and it is an unqualified product; The "crack" explosion during combustion indicates that the water content of the oil is seriously exceeding the standard, and it may be adulterated products, so it is absolutely impossible to buy.
  Five questions. Ask the merchant about the purchase channel, ask for the purchase invoice or check the sampling test report of the local food hygiene supervision department if necessary. (Comprehensive by this newspaper)

A new virus spoofs Python digital signature to trick users into entering the back door.

Recently, Rising Security Research Institute captured a batch of malicious software with fake Python digital signatures. Attackers disguised these malicious software, induced users to download and run the Farfli backdoor program through websites and email links, and finally achieved the purpose of remotely controlling users’ computers and stealing private information.

Recently, Rising Security Research Institute captured a batch of malicious software with fake Python digital signatures. Attackers disguised these malicious software, induced users to download and run the Farfli backdoor program through websites and email links, and finally achieved the purpose of remotely controlling users’ computers and stealing private information.

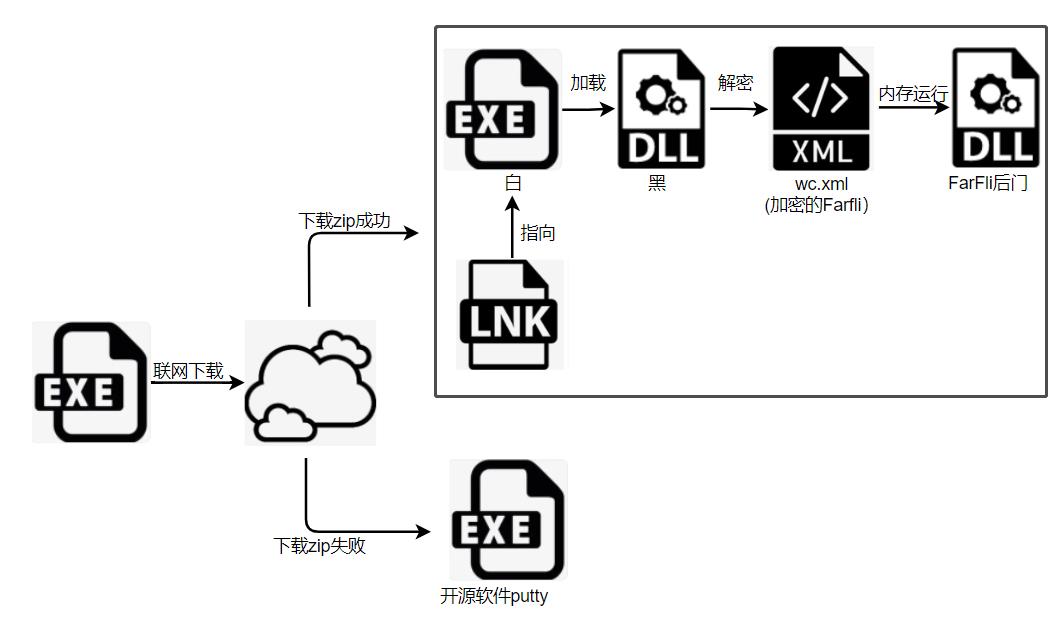
Figure: Attack process

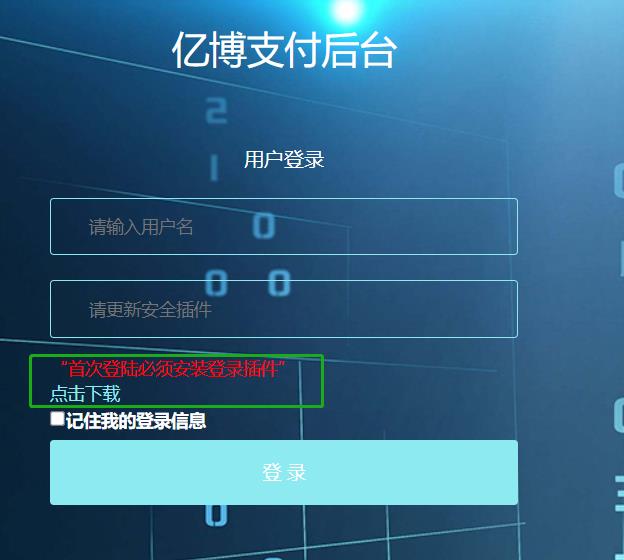
Rising security experts made a detailed analysis of the malware, and found that the malware with a fake Python digital signature appeared in a gambling payment website, which showed that "login plug-in must be installed for the first login", and when the user clicked, the malware would be downloaded.

Figure: Screenshot of website page

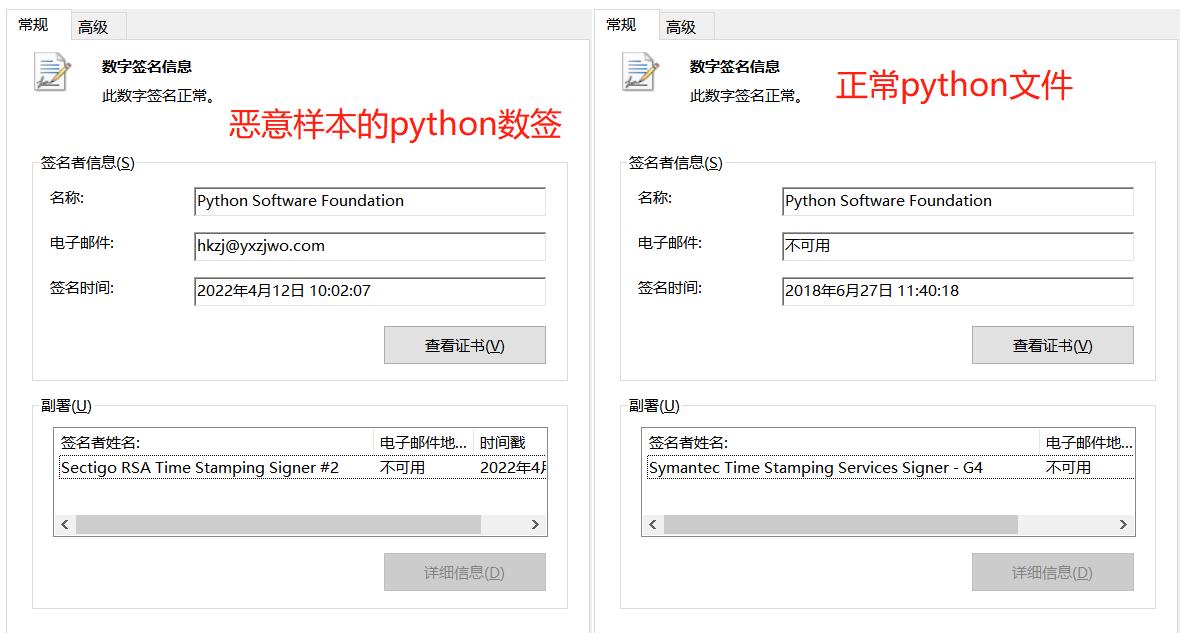
According to Rising security experts, this malicious software with a fake Python digital signature has a strong camouflage. The effective digital signature is very similar to the normal Python file digital signature. The names of the signers are Python Software Foundation, and only the email information is inconsistent, which is an address that has nothing to do with Python.

Figure: Digital signature comparison

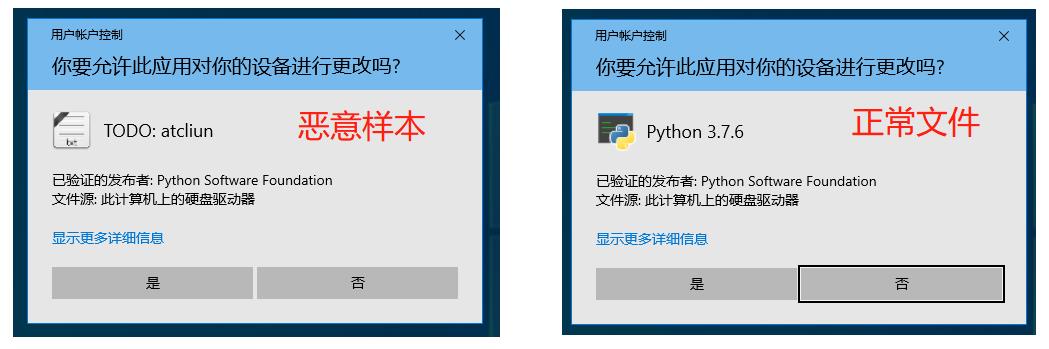
Moreover, when the user clicks to run the malware, its UAC pop-up window is not much different from that of the normal Python file, and only the signer name Python Software Foundation appears by default. Therefore, it is extremely difficult for users to judge whether this file is normal by digital signature.

Figure: UAC pop-up window comparison

Rising security experts said that these confusing operations in the early stage were only the foreshadowing, and the attacker’s ultimate goal was to let the user download the compressed package with the remote control Trojan in Youdao cloud notes through this disguised malicious program, and the compressed package contained normal exe files, dll malicious files and encrypted Farfli backdoor programs. Therefore, as long as the user clicks execute Exe, the dll will be loaded, which will decrypt the Farfli backdoor program and make it run secretly in the memory, and the user’s computer will face the risks of file theft, remote control, keyboard recording, camera being viewed and so on.

Because the malicious software of this fake Python digital signature is very disguised and difficult for users to distinguish, Rising security experts remind users to pay attention to the following points:

1. Don’t open suspicious files

Do not open suspicious files and emails from unknown sources to prevent social engineering and phishing attacks.

2. Deploy gateway security products such as network security situational awareness and early warning system.

Gateway security products can use threat intelligence to trace the threat behavior track, help users to analyze the threat behavior, locate the source and purpose of the threat, trace the means and path of the attack, solve the network threat from the source, find the attacked node to the maximum extent, and help enterprises to respond and deal with it faster.

3. Install effective antivirus software to intercept and kill malicious documents and Trojan viruses.

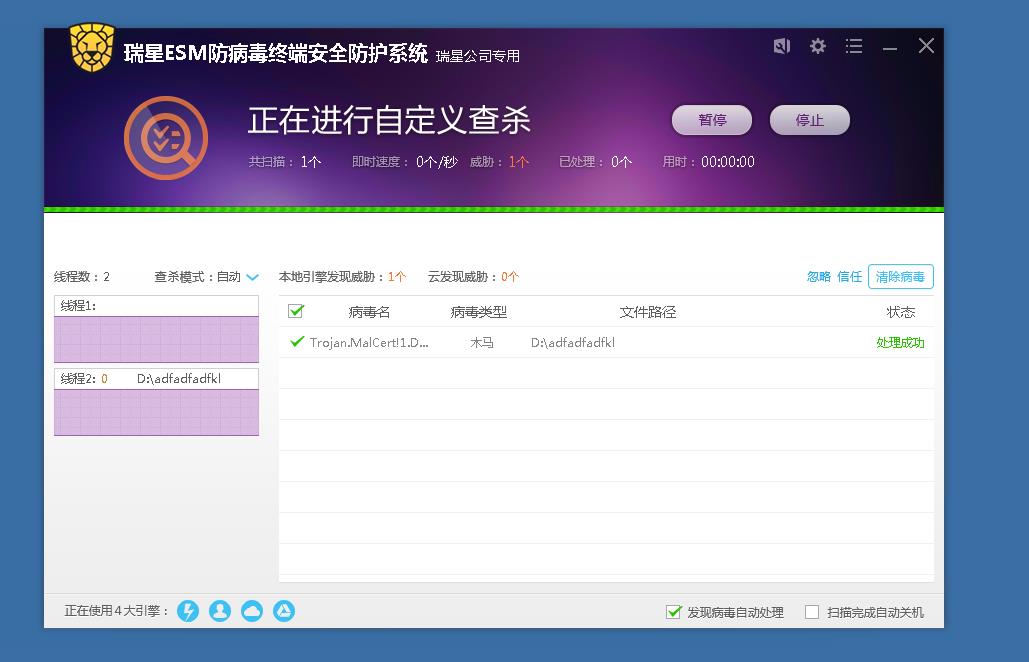
Anti-virus software can intercept malicious documents and Trojan viruses. If users accidentally download malicious files, anti-virus software can intercept killing, prevent viruses from running, and protect users’ terminal security. At present, Rising ESM anti-virus terminal security protection system can intercept and kill such malicious software, and users can install and use it to avoid risks.

Figure: Rising ESM anti-virus terminal security protection system kills the corresponding virus.

4. Install system patches and important software patches in time.

Many malicious software often uses known system vulnerabilities and software vulnerabilities to spread, and installing patches in time will effectively reduce the impact of vulnerability attacks.

5. Use strong passwords instead of weak passwords such as "123456", especially for devices that are open on the external network.

Weak passwords, like vulnerabilities, are often used by attackers and malware to spread and invade, and using high-strength passwords will block this attack.